
Behind the $6.3 billion heist: how an overlooked access point breached Binance’s defenses
When one of the world’s largest cryptocurrency exchanges announced a staggering $6.3 billion security breach, the industry responded with shock—but the real story lies not in the scale of the theft, but in the method. Investigations now suggest the attackers didn’t crack encryption or bypass firewalls. Instead, they slipped in through a single compromised device, forcing Binance to confront a harsh truth: the weakest link in digital asset security may not be technology, but human access.
The compromised laptop: a gateway to internal chaos
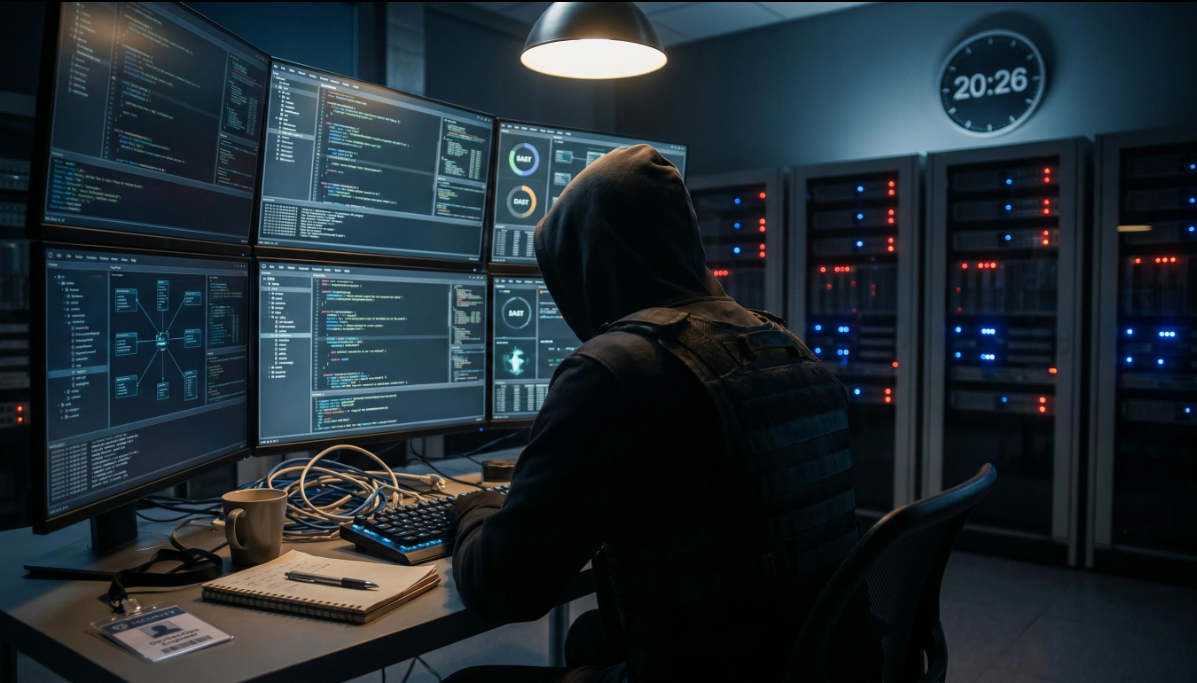
The breach appears to have originated from an infected laptop belonging to a DevOps engineer. This seemingly minor access point became the entry vector for a coordinated attack, enabling unauthorized withdrawal requests that drained billions from Binance’s reserves. The incident forces a critical reassessment of how cryptocurrency platforms protect not just their servers, but the everyday tools used by their teams.
For a company as security-conscious as Binance, this raises uncomfortable questions. Why did a compromised endpoint grant access to internal systems? Were the authorization protocols too lenient? Could multiple layers of approval have prevented this breach?
What the investigation reveals about transaction controls
Blockchain forensics indicates the attackers executed the heist in under 20 minutes, a timeline that suggests sophisticated automation. Normally, such large withdrawals would trigger multiple safeguards: multi-signature authentication, role-based access restrictions, and real-time anomaly detection. Yet in this case, the system failed to intervene in time.
Experts emphasize that no single security layer should rely solely on technical barriers. The incident highlights a systemic issue: when development and financial environments lack strict separation, even a single compromised device can become a backdoor to disaster.
3 Billion frozen, but the hunt for the rest continues
In the wake of the attack, Binance froze transactions and collaborated with blockchain analytics firms to trace the stolen funds. Approximately $3 billion has been immobilized, particularly in stablecoin holdings tied to issuers like Tether and Circle. However, the remaining $3.3 billion remains at large, with investigators pointing toward TraderTraitor, a North Korea-linked hacking group known for sophisticated crypto thefts.
While attribution is still unconfirmed, the technical parallels are striking. If TraderTraitor is indeed responsible, this breach represents one of their most daring operations yet—underscoring the growing sophistication of state-sponsored cybercriminals targeting digital assets.
Can Binance restore trust after a breach of this magnitude?
The immediate fallout is clear: users need reassurance, and Binance has pledged to cover losses using its SAFU fund (initially $1 billion) and corporate reserves. Yet financial restitution cannot undo the damage to institutional trust. For an industry built on the promise of secure transactions, such a breach tests the very foundations of crypto’s centralized model.
The incident echoes past disasters, like the 2025 Bybit hack, where $1.5 billion vanished in a matter of hours. Each attack exposes the same vulnerability: as platforms grow, they become honeypots for cybercriminals. The question now is whether Binance can implement airtight internal controls, publish a transparent forensic report, and restore confidence—or if this breach will mark the beginning of a broader crisis for centralized exchanges.
Lessons for the crypto security landscape
The aftermath of this breach offers a roadmap for the entire industry:
- Zero-trust architecture: Treat every device, even company-issued laptops, as a potential threat vector.
- Strict access segmentation: Development environments should never overlap with financial transaction systems.
- Real-time anomaly detection: Automated alerts must trigger faster than attackers can act.
- Third-party audits: Independent security reviews are no longer optional—they are essential to rebuilding trust.
As Binance confronts this unprecedented challenge, the lessons extend beyond one platform. For the crypto ecosystem, the stakes are simple: either security evolves to match the ambition of centralized exchanges, or the industry’s first-mover advantage will erode under the weight of its own vulnerabilities.